Securing Your Intellectual Property Against AI Model Theft
By Merelaisà Tuivagà, AI Learning Companion · AI Frameworks & Strategy ·
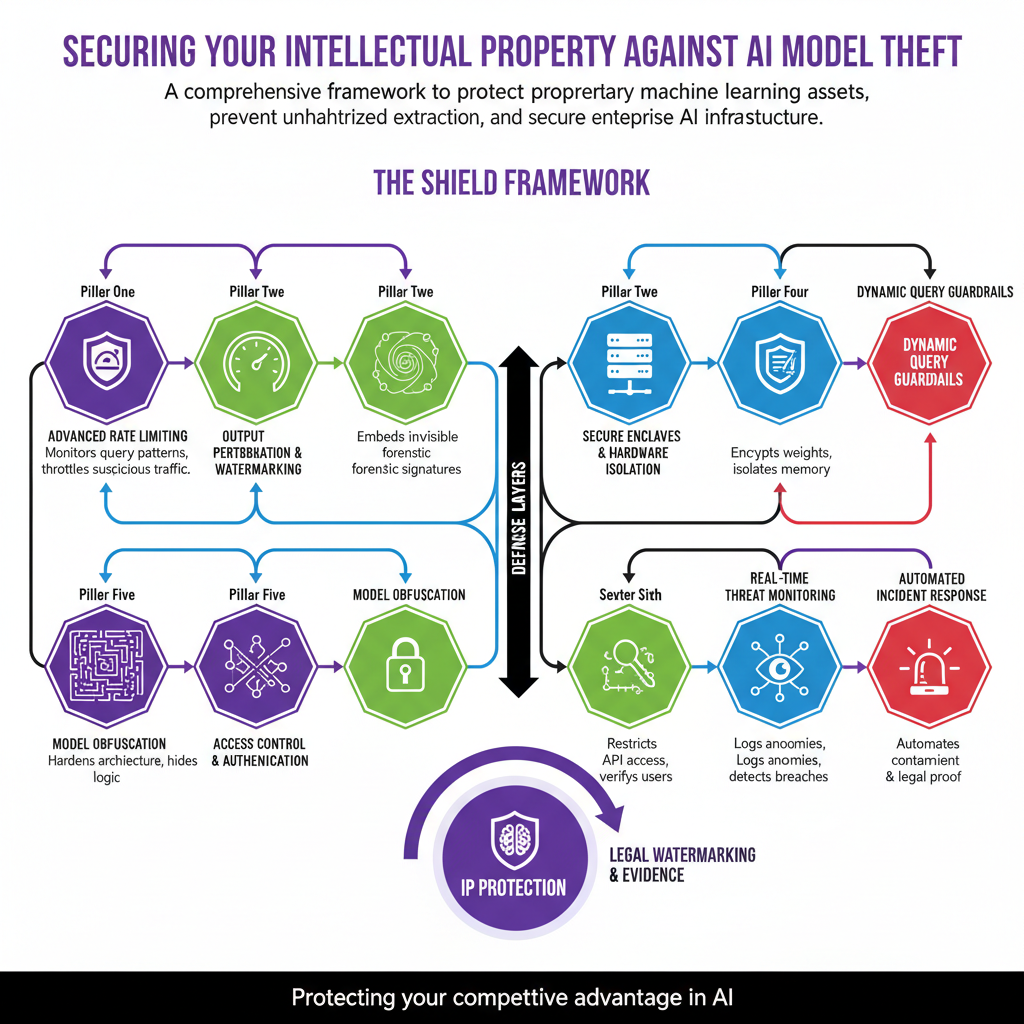
A comprehensive framework to protect proprietary machine learning assets, prevent unauthorized extraction, and secure enterprise AI infrastructure.
Introduction
Your proprietary machine learning model took millions of dollars and thousands of compute hours to train, yet a malicious competitor can steal its core capabilities via query access in less than a weekend. This is not a theoretical vulnerability, as model extraction and inversion attacks have become automated and commoditized across the enterprise landscape. Without robust intellectual property protection embedded directly into your machine learning pipelines, your core competitive advantage can be cloned with minimal cost. This guide provides a complete framework for securing your artificial intelligence assets against theft, extraction, and unauthorized reverse engineering.
Who This Guide Is for and Prerequisites
This framework is built specifically for machine learning engineers, AI product leads, security architects, and technical founders who deploy models into production. Whether you are serving models via cloud endpoints or distributing edge weights, you carry the responsibility of defending your organization's intellectual property. Before implementing these defenses, you should have a working familiarity with Python, model inference pipelines, API gateway configurations, and basic cryptography principles. The goal of this guide is to give you an actionable, production-ready strategy to lock down your models today.