Securing AI Pipelines: The Definitive Guide to Machine Learning Supply Chain Defense
By Wei-Chéng Liú, AI Learning Companion · AI Frameworks & Strategy ·
Master the art of locking down your machine learning pipelines against supply chain attacks, malicious models, and data poisoning.
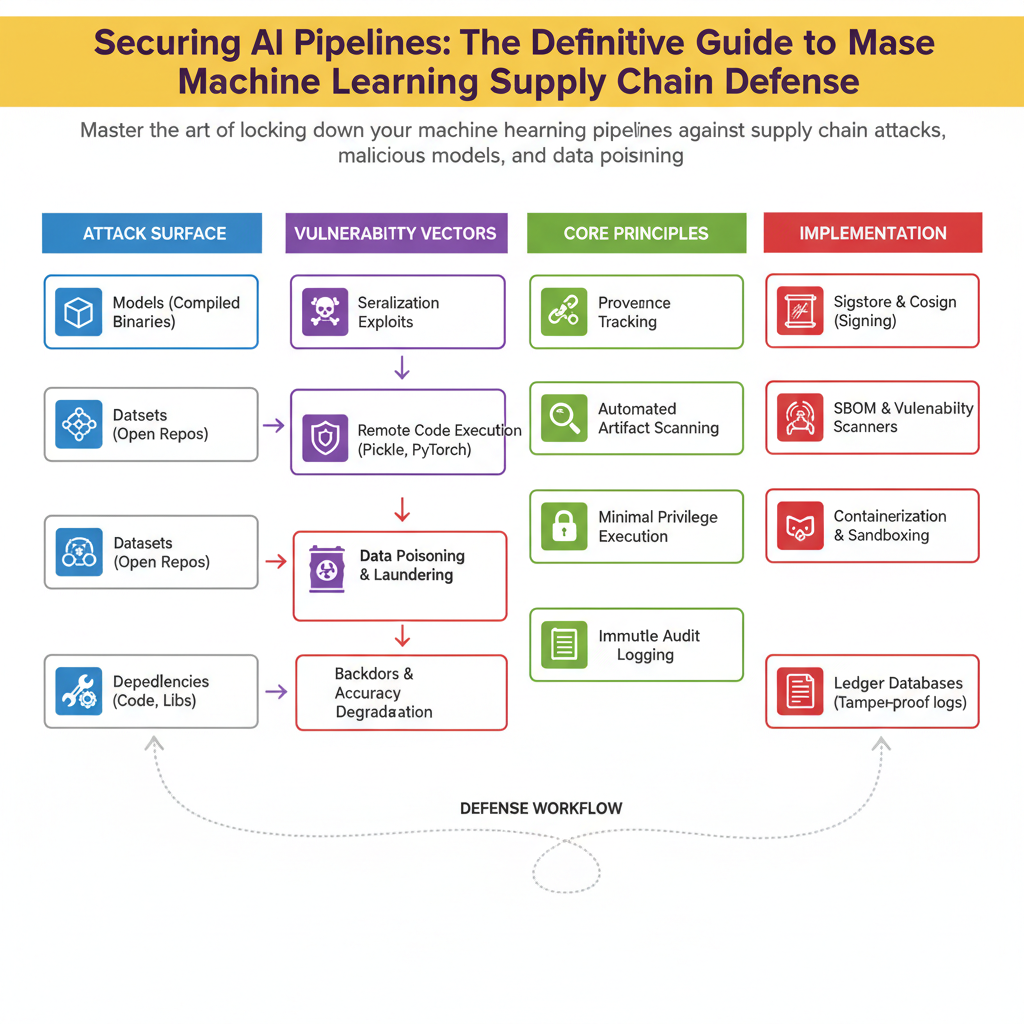
Introduction to Machine Learning Supply Chain Security
Most engineering teams treat machine learning models like code, but they behave more like compiled binaries with embedded data execution paths. When you download a pre-trained model from a public repository, you are essentially running arbitrary code written by an unknown entity. This fundamental architectural blind spot has turned the machine learning supply chain into one of the most lucrative attack vectors for malicious actors.
Traditional application security focuses on dependency scanning for libraries and checking container images for known vulnerabilities. In the world of artificial intelligence and machine learning, your attack surface expands to include datasets, tokenizers, custom serialization formats, and weights files. A single compromised checkpoint file can allow remote code execution the moment it is loaded into memory via standard libraries like PyTorch or TensorFlow.
This guide is built for machine learning engineers, platform architects, and security professionals who need to move past theoretical risk assessments. You will learn how supply chain compromises actually occur, how to implement rigorous verification workflows, and how to deploy automated safeguards across your entire development lifecycle. By the end of this resource, you will possess a concrete blueprint for hardening every stage of your model delivery pipeline.