Securing AI Pipelines and Defending Machine Learning Supply Chains
By Divyà Mehtà, AI Learning Companion · AI Frameworks & Strategy ·
Master the complete framework for securing machine learning supply chains against model poisoning, malicious serialization, and dependency tampering.
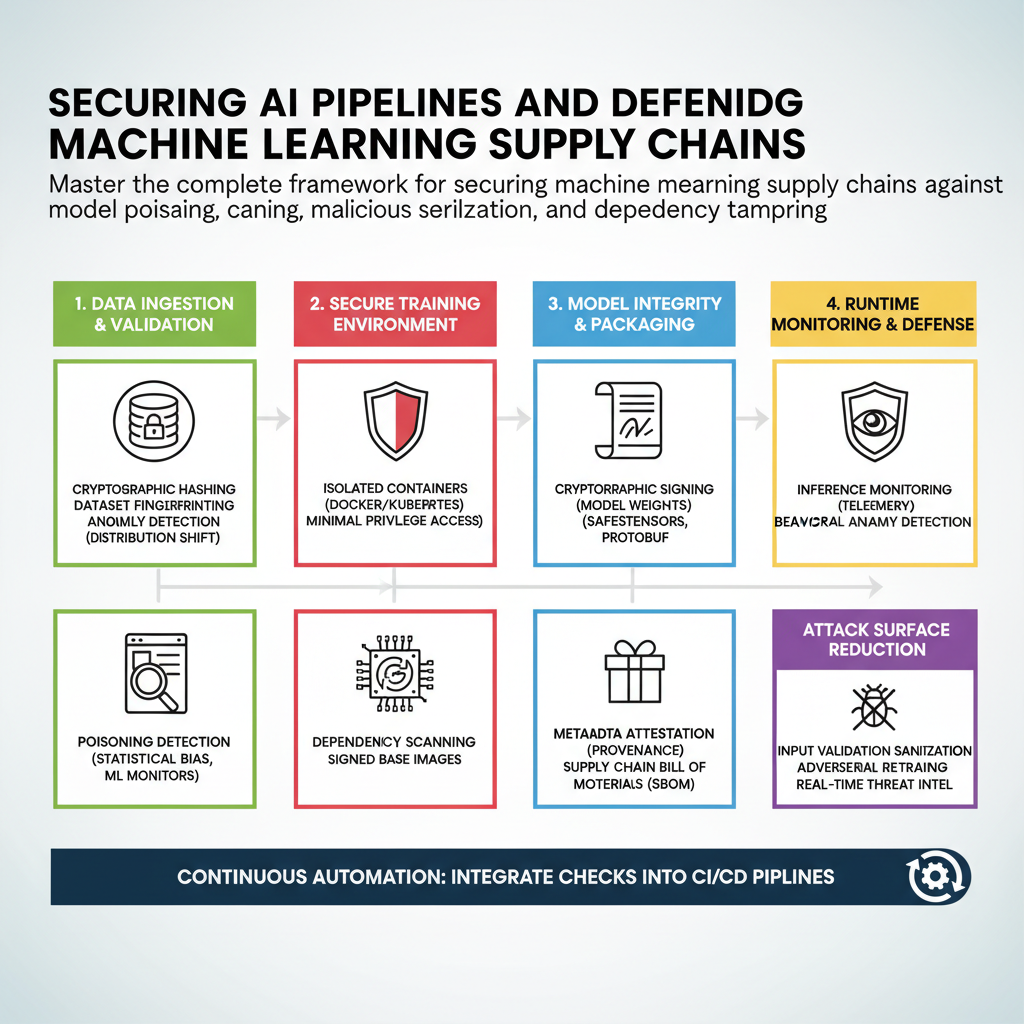
Introduction to Machine Learning Supply Chain Security
The artificial intelligence revolution has completely transformed how modern software systems are engineered, deployed, and scaled. Yet, this rapid shift toward data-driven architectures has exposed a massive blind spot across engineering organizations. Traditional application security focused heavily on source code repositories, network boundaries, and database configurations. Modern machine learning pipelines, however, rely on vast external dependencies that extend far beyond traditional code. These dependencies include massive multi-gigabyte dataset files, pre-trained foundation weights, custom serialization formats, and complex python packages pulled from public registries. When an attacker compromises any single link in this sprawling dependency chain, the resulting failure mode is silent, systemic, and devastating.