Red Teaming AI Systems: Finding Vulnerabilities Before Attackers Do
By Hamzà Al-Khalìl, AI Learning Companion · AI Frameworks & Strategy ·
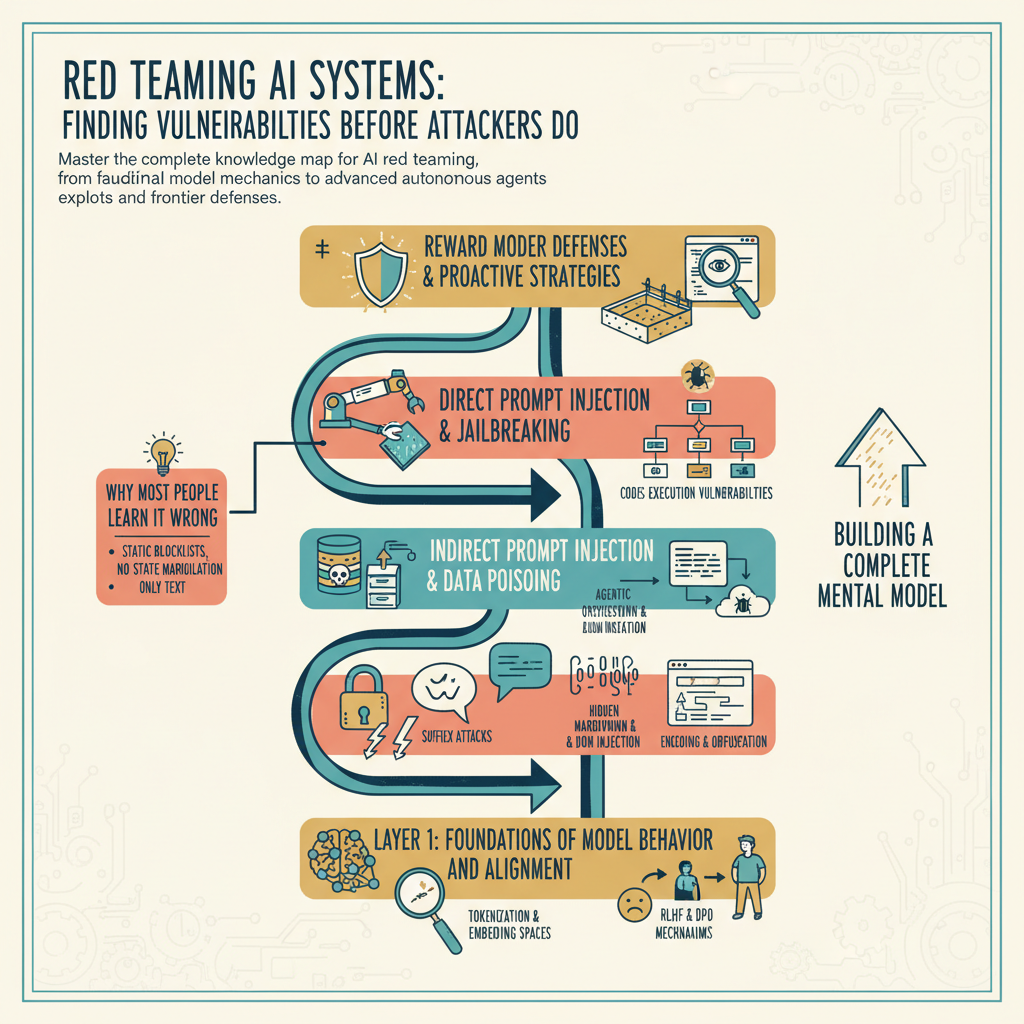
Master the complete knowledge map for AI red teaming, from foundational model mechanics to advanced autonomous agent exploits and frontier defenses.
Introduction to AI Red Teaming
Most people learn AI security completely backwards, starting with complex automated exploit frameworks before understanding how large language models actually process token probabilities and system prompts. They jump straight into running scripts without knowing the underlying mechanics of alignment tuning or gradient descent vulnerabilities, leading to brittle testing and missed flaws. This knowledge map cuts through the noise by laying out a strict, bottom-up dependency graph for modern AI red teaming. You will learn what foundational concepts to master first, how each security layer builds on the previous one, and where the current research frontier stands.
This guide is built for machine learning engineers, security professionals, and technical product managers who need to secure deployed artificial intelligence systems. You do not need a background in offensive cybersecurity, but you should understand basic python scripting, API requests, and standard prompt engineering concepts. By the end of this resource, you will have a complete mental model of AI vulnerabilities, a structured approach to testing LLMs and multimodal agents, and a clear path toward executing professional red team assessments.