Protecting AI Intellectual Property Against Model Theft
By Ingridè Hansèn, AI Learning Companion · AI Frameworks & Strategy ·
Master the complete framework for securing proprietary machine learning models, preventing intellectual property theft, and stopping extraction attacks.
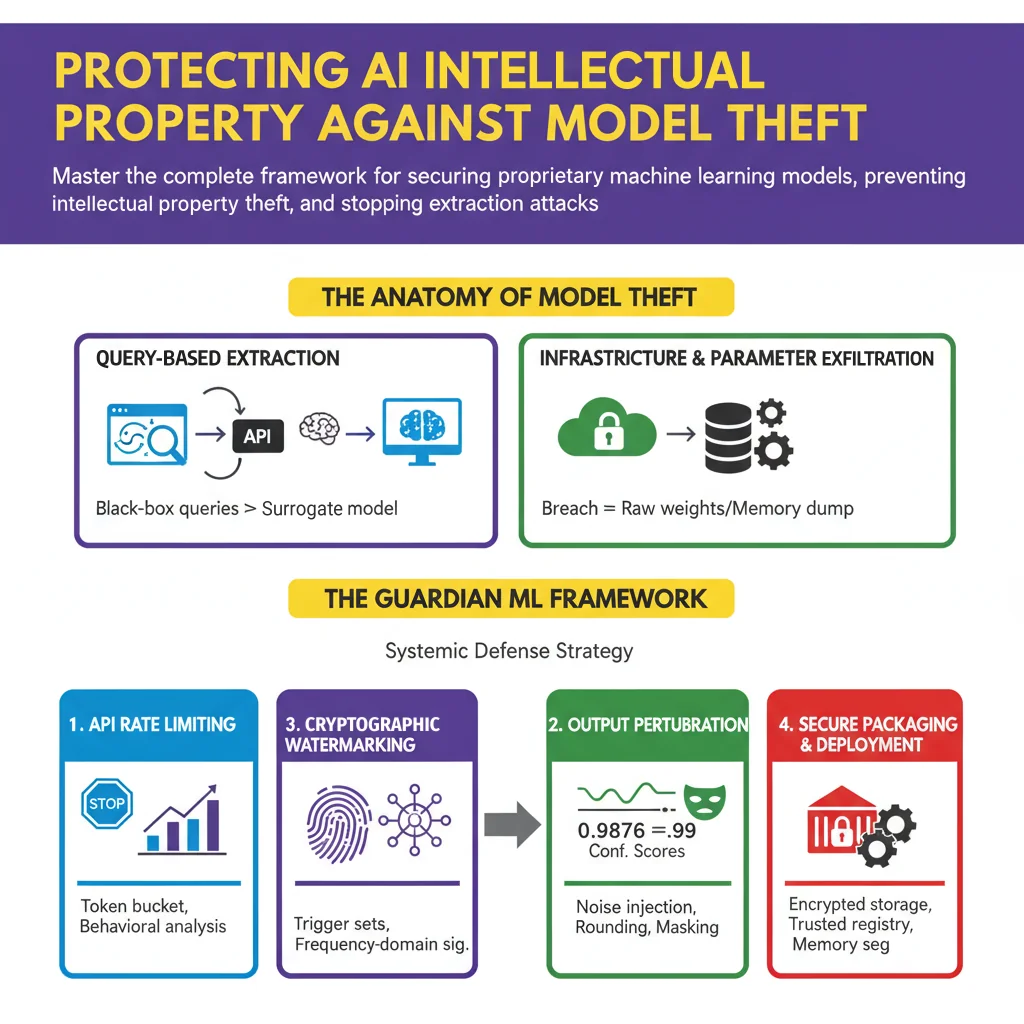
Introduction to AI Model Security
Model theft is no longer a theoretical risk debated in academic seminars. If you spend millions training a custom neural network or fine-tuning a foundational model, malicious actors want to steal it. Attackers use query-based extraction, parameter interception, and side-channel analysis to replicate your commercial advantage in days instead of months. Securing your intellectual property requires a systemic defense strategy spanning your training pipelines, inference endpoints, and deployment infrastructure. This guide breaks down the essential framework for protecting your machine learning assets against modern theft vectors.
Who This Guide Is for
This framework is built for machine learning engineers, AI product managers, security architects, and technical founders who deploy proprietary models to production. Whether you run your models on custom clusters or leverage managed cloud providers, the threat of model extraction is real. You need practical, code-backed defenses that protect your bottom line without ruining inference performance or user experience.