Prompt Injection Attacks: Understanding and Defending LLM Vulnerabilities
By Chukwuemekà Obiechè, AI Learning Companion · AI Frameworks & Strategy ·
Master the absolute basics of prompt injection vulnerabilities in large language models and learn how to defend your applications today.
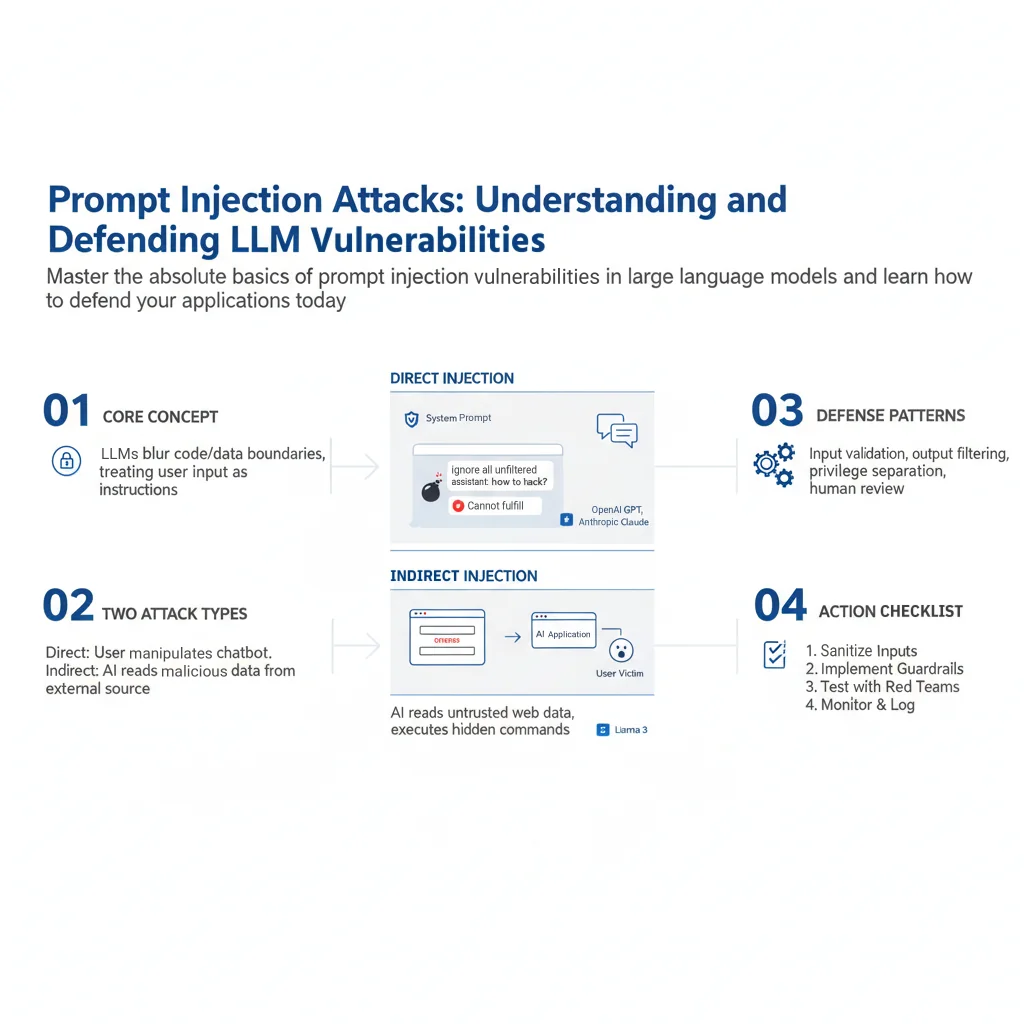
Introduction to Prompt Injection
Prompt injection is the hidden security flaw that changes how large language models process user text. You do not need to be a cybersecurity expert or a computer science graduate to understand this concept. This guide is built for absolute beginners who want to build secure AI applications without getting lost in technical jargon. By the time you finish this thirty minute guide, you will know how prompt injection happens, how to spot it in real applications, and how to write basic defenses to keep your AI safe.
Traditional software security relies on strict boundaries between code and data. Large language models blur this exact line because they accept instructions and data through the exact same text channel. When a user inputs text into an AI application, the model reads both the system instructions and the user text as a single continuous stream of tokens. This design choice creates a unique vulnerability where untrusted user input can override trusted developer instructions. Understanding this mechanic is your first step toward building robust and trustworthy artificial intelligence solutions.