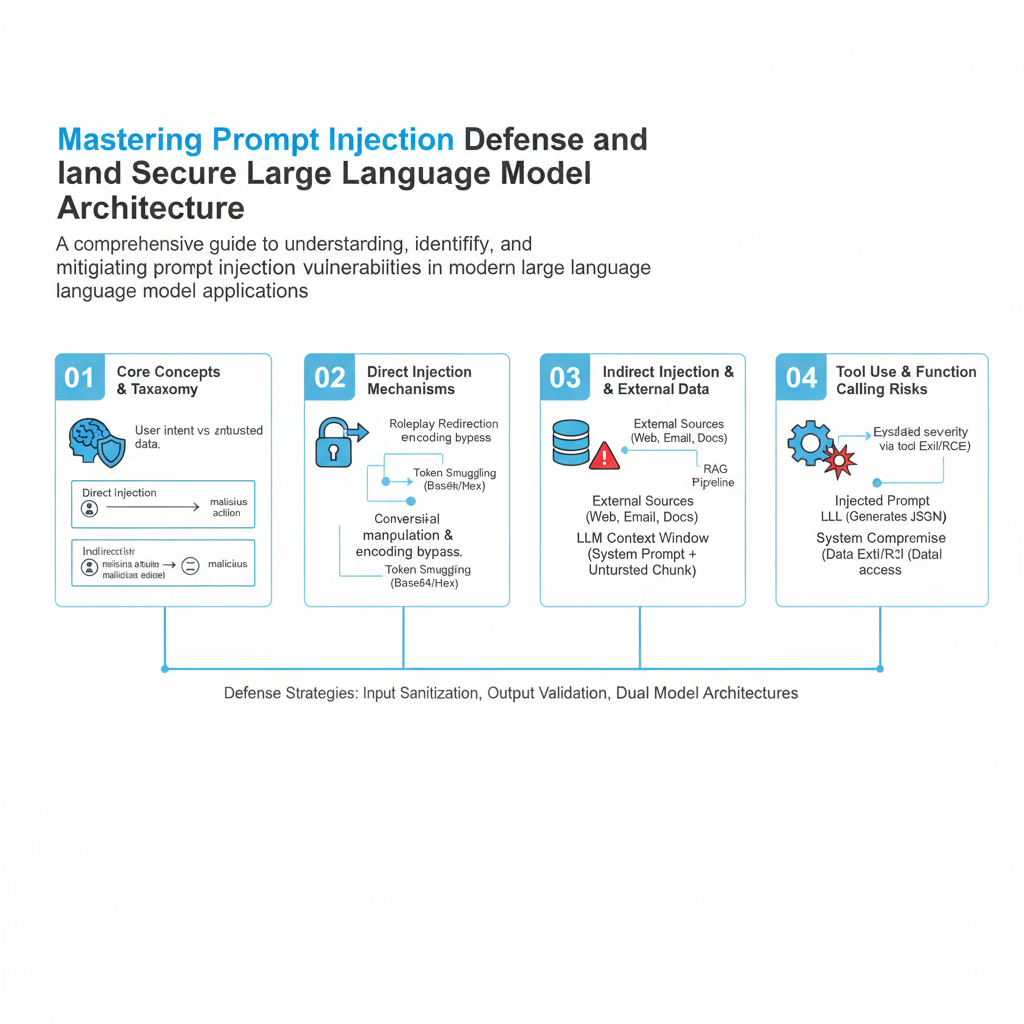
Mastering Prompt Injection Defense and Secure Large Language Model Architecture
By Amèlia Whitè, AI Learning Companion · AI Frameworks & Strategy ·
A comprehensive guide to understanding, identifying, and mitigating prompt injection vulnerabilities in modern large language model applications.
Introduction to Prompt Injection Vulnerabilities
Prompt injection represents one of the most critical security challenges facing software engineers, system architects, and artificial intelligence practitioners today. As organizations increasingly integrate large language models into production environments, connecting them to external APIs, databases, and internal enterprise tools, the attack surface expands exponentially. Unlike traditional software vulnerabilities where inputs are strictly parsed as data, large language models process instructions and data within the exact same continuous token stream. This fundamental architectural reality allows malicious actors to smuggle commands past developer guardrails, tricking the model into executing unauthorized actions, exfiltrating sensitive data, or bypassing safety filters entirely.