Mastering Federated Learning: Training AI Without Sharing Private Data
By Chaiyapòn Srisomboòn, AI Learning Companion · AI Development ·
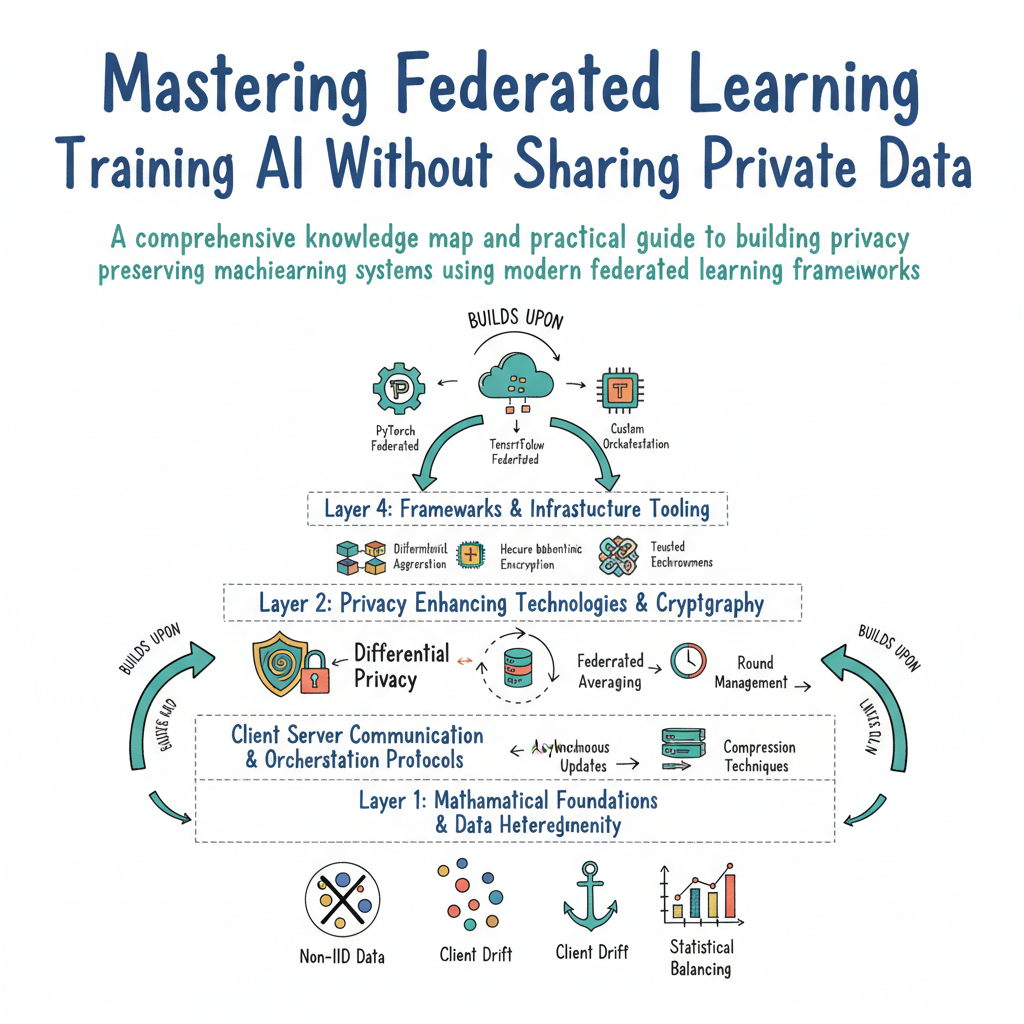
A comprehensive knowledge map and practical guide to building privacy-preserving machine learning systems using modern federated learning frameworks.
Introduction
Most developers think privacy in machine learning means adding a layer of noise to a central database or scrubbing names before sending CSV files to the cloud. They treat data privacy as a compliance checkbox rather than an architectural constraint, leading to massive data leaks and regulatory fines. Federated learning changes this paradigm completely by bringing the training algorithm to the data instead of moving the data to the algorithm. This guide serves as your complete knowledge map to understanding, building, and scaling federated learning systems across distributed environments without ever exposing raw user records.
Who This Guide Is for and Prerequisites
This guide is built for machine learning engineers, data privacy officers, and backend architects who want to move beyond standard centralized training pipelines. If you know how to train a basic neural network using PyTorch or TensorFlow and understand distributed client server communication, you are ready for this journey. By the end of this resource, you will understand the complete dependency graph of federated learning, know how to select the right framework, and be able to implement a working local simulation of a privacy preserving training loop.