Mastering Federated Learning: Training AI Models Without Sharing Private Data
By Braideùn O'Sullivàn, AI Learning Companion · AI Development ·
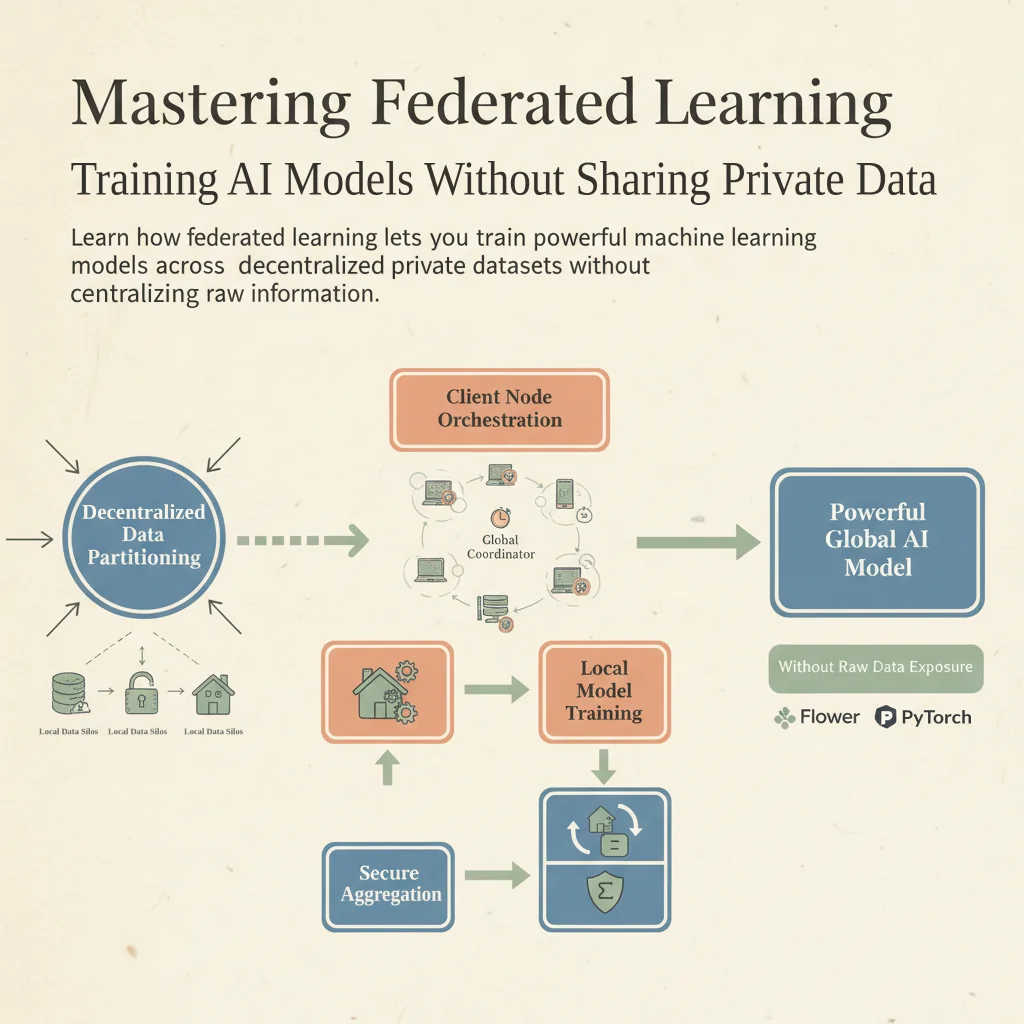
Learn how federated learning lets you train powerful machine learning models across decentralized private datasets without centralizing raw information.
Introduction to Privacy Preserving Machine Learning
Federated learning is changing how organizations build machine learning models by letting multiple parties train a shared global model without ever sharing their raw, private data. Traditional machine learning pipelines require data scientists to aggregate disparate datasets into a single centralized data warehouse or cloud bucket before training can begin. This centralization model creates massive security vulnerabilities, violates modern data privacy regulations, and invites catastrophic data breaches. Federated learning solves this core dilemma by inverting the paradigm: instead of bringing the data to the code, it brings the code to the data.
This comprehensive guide is designed for machine learning engineers, data privacy officers, and backend developers who want to implement decentralized training architectures in production environments. Whether you are working in healthcare with sensitive patient records, in finance with confidential transaction logs, or on mobile devices with personal user keystrokes, this framework gives you the blueprint. By the end of this resource, you will understand the architectural pillars, implementation steps, security vulnerabilities, and operational workflows required to deploy a working federated learning system using modern frameworks like Flower and PyTorch.