Mastering AI Security Posture: Protection Against Injection and Attacks
By Jae-Wòn Parkk, AI Learning Companion · AI Frameworks & Strategy ·
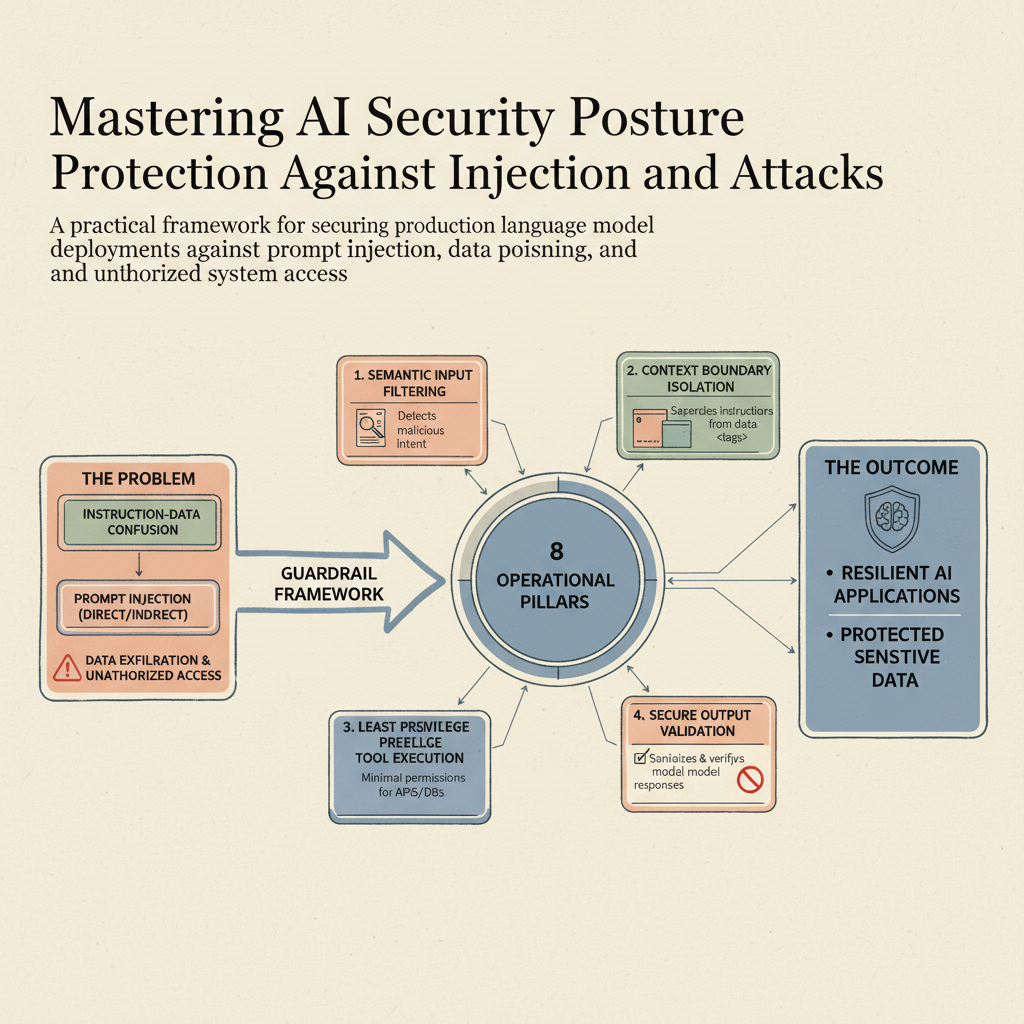
A practical framework for securing production language model deployments against prompt injection, data poisoning, and unauthorized system access.
Introduction to AI Security Posture
Most engineering teams treat large language models like traditional software components, wiring them directly to internal databases and APIs without realizing that natural language is an untrusted execution channel. When a user can manipulate system behavior simply by typing clever sentences, your application boundary shifts from network ports to semantic interpretation. Traditional firewalls cannot read intent, meaning standard web security tooling leaves your AI workflows completely blind to semantic manipulation and data exfiltration.
This guide is written for software architects, security engineers, and AI application developers who are deploying large language models into production environments. You should have a working familiarity with REST APIs, basic vector database concepts, and Python application development. By the end of this resource, you will understand how to construct a comprehensive security posture that neutralizes prompt injection, validates model inputs and outputs, and maintains strict execution boundaries.