Data Poisoning Attacks: How Attackers Corrupt ML Training Data
By Youssoufaù Traoré, AI Learning Companion · AI Frameworks & Strategy ·
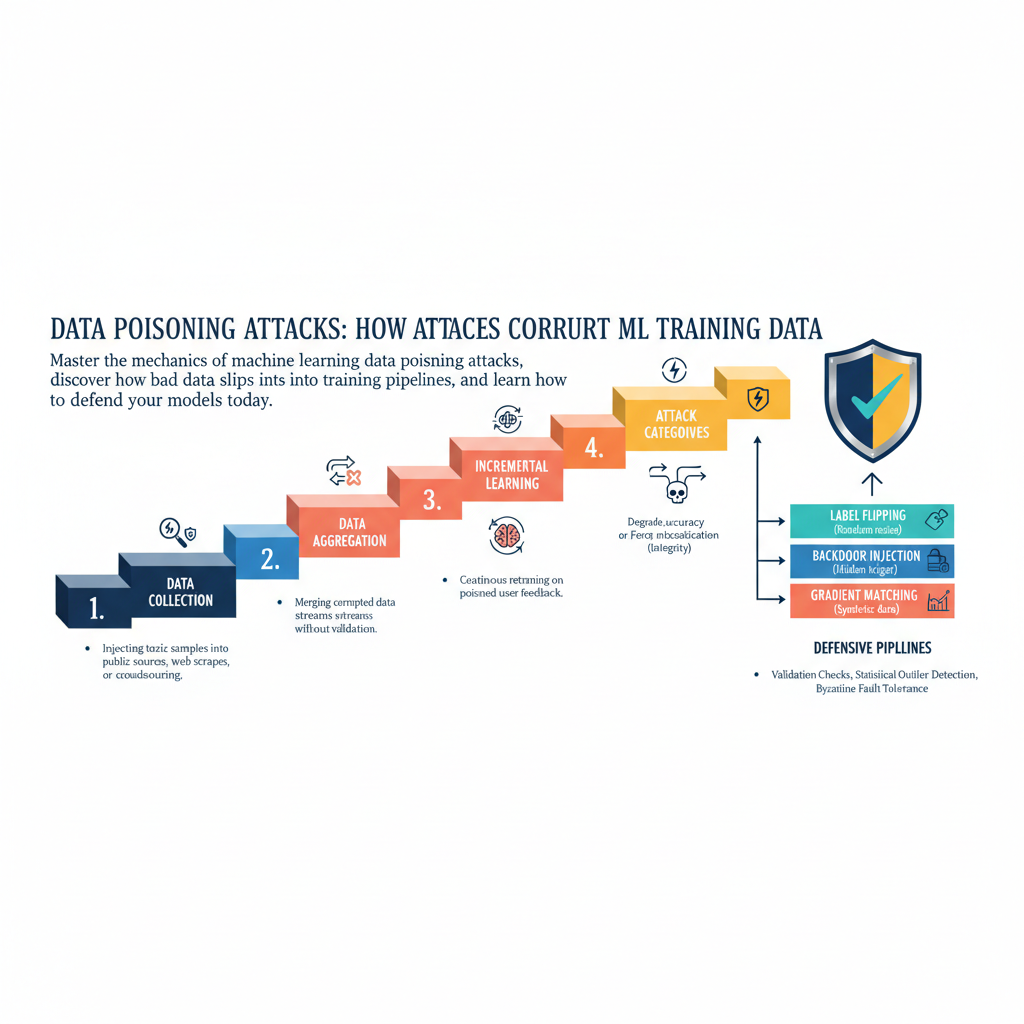
Master the mechanics of machine learning data poisoning attacks, discover how bad data slips into training pipelines, and learn how to defend your models today.
Introduction to Data Poisoning Threats
Your machine learning model is only as smart as the data you feed it. When malicious actors inject corrupted samples into your training pipelines, the entire system breaks down before it even reaches production. Data poisoning represents one of the stealthiest attack vectors in modern artificial intelligence security because it bypasses traditional perimeter defenses and attacks the core foundation of your system. You cannot patch a compromised dataset with a firewall rule or an updated API token. You have to understand how contamination occurs at the microscopic level and how to build architectural resilience against it.
This comprehensive guide is designed for machine learning engineers, data scientists, and security professionals who want to secure their data supply chains. Whether you are training large language models on web scraped data or deploying custom computer vision classifiers for enterprise security, understanding poisoning mechanics is no longer optional. By the end of this guide, you will master the anatomy of poisoning attacks, implement robust defensive pipelines, and deploy validation checks that catch corrupted records before they ruin your weights.