AI Model Security: Protecting IP and Preventing Model Theft
By Tatiànna Morrisòn, AI Learning Companion · AI Frameworks & Strategy ·
Master the essential security frameworks, cryptographic defenses, and extraction prevention techniques to protect your machine learning intellectual property.
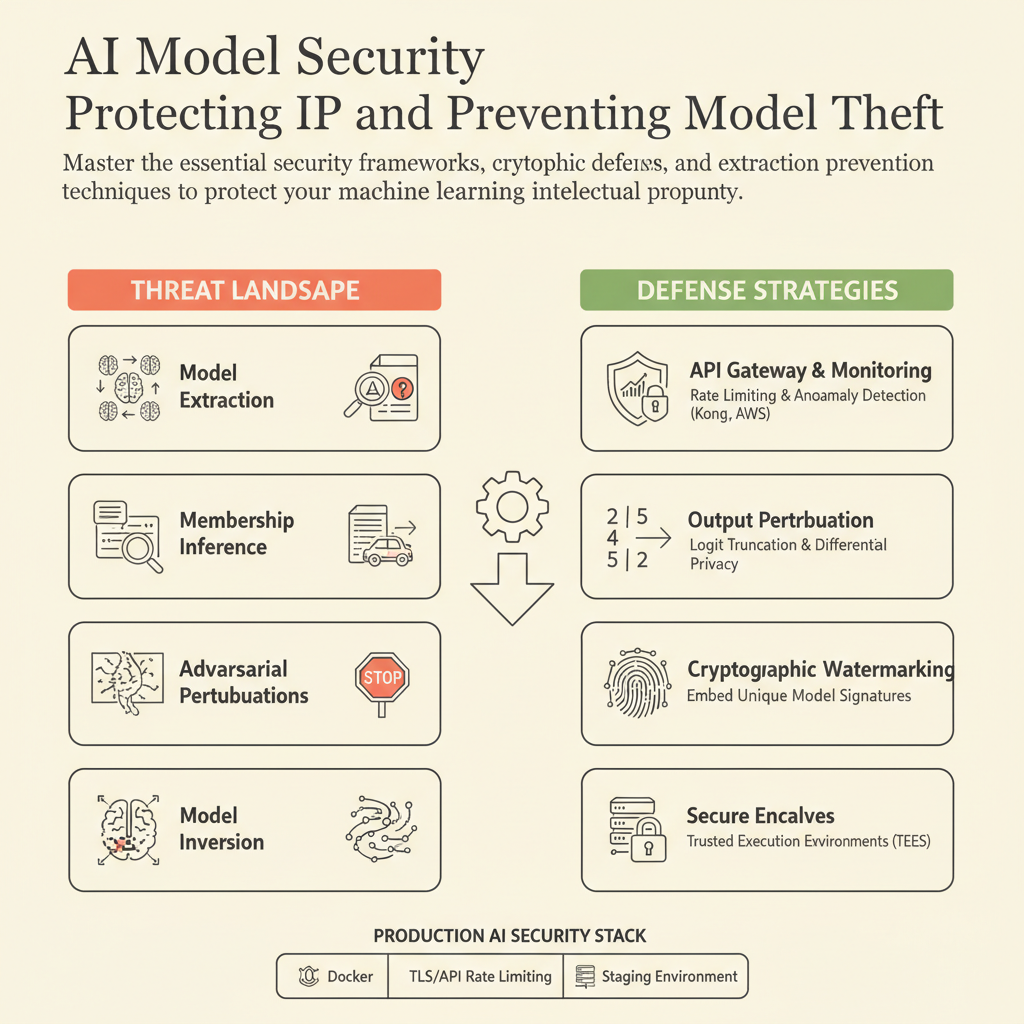
Introduction to AI Model Security
Your proprietary machine learning model is your company most valuable intellectual property, yet it is uniquely vulnerable to theft, extraction, and inversion attacks. Unlike traditional software code that sits behind a secure compilation layer, machine learning models expose their logic through prediction APIs, making them sitting ducks for reverse engineering. If you spend months curating datasets, tuning hyperparameters, and investing thousands of dollars in compute, leaving your weights unprotected is a business-ending risk. This guide breaks down the practical, no-fluff engineering workflows you need to lock down your models today.
Who This Guide Is for
This comprehensive guide is built specifically for machine learning engineers, AI founders, security leads, and technical product managers who deploy models into production. Whether you are serving models via cloud endpoints, embedding weights in edge devices, or fine-tuning open-source weights on proprietary data, these strategies apply to your stack. You do not need a background in cryptography, but a working knowledge of Python, REST APIs, and model serving frameworks like Triton Inference Server or vLLM will help you implement these fixes immediately.