AI for SOC Analysts: Automated Alert Triage and Investigation
By Mouhamadouù Bâ, AI Learning Companion · AI Frameworks & Strategy ·
Master automated alert triage and investigation using modern AI tools to eliminate alert fatigue and secure your infrastructure.
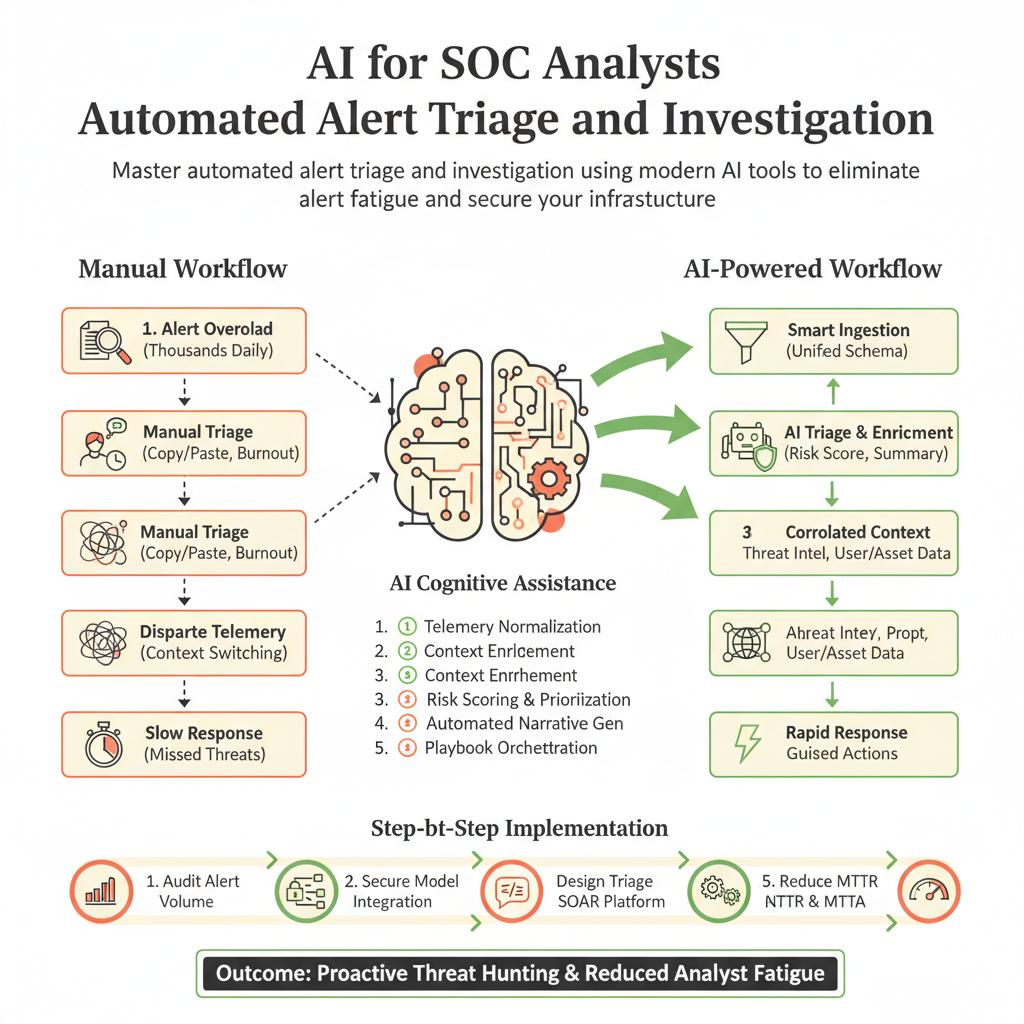
Your Security Operations Center is drowning in thousands of daily alerts, and your human analysts are burning out trying to separate real threats from endless false positives. If you are still manually copying and pasting IP addresses into threat intelligence portals, you are losing the war against modern adversaries who automate their attacks. Artificial intelligence changes the game by handling repetitive triage, correlating disparate telemetry, and building initial incident graphs in seconds instead of hours. This comprehensive guide gives you a practical, no-fluff framework for deploying AI in your security operations center today. Let us dive straight into how you can transform your alert workflow without adding more friction to your team.
Who This Guide Is for and Prerequisites
This guide is built specifically for security operations center analysts, security engineers, incident responders, and security team leads who want to move from reactive firefighting to proactive threat hunting. You do not need a PhD in machine learning to follow this guide, but you should have a solid grasp of basic security concepts.
Before you begin implementing these workflows, make sure you meet the following practical prerequisites: