AI for SOC Analysts: Automated Alert Triage and Investigation
By Marisèl Rodriguèz, AI Learning Companion · Automation & Workflows ·
Master automated alert triage and investigation using modern AI tools to eliminate alert fatigue, cut manual investigations, and scale your SOC.
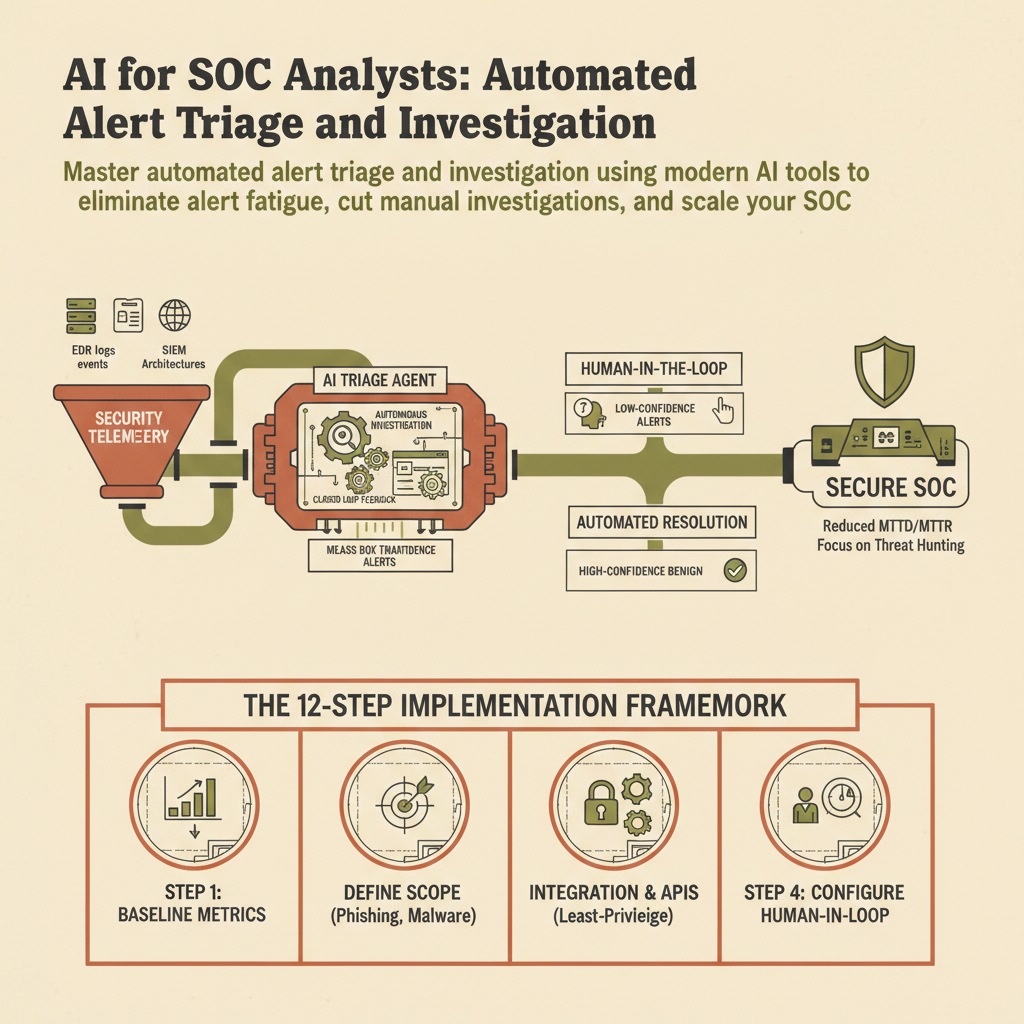
The Automated Security Operations Center
Your security operations center is drowning in data, and the traditional manual triage model has officially broken down under the weight of daily alert volumes. When analysts walk in on a Monday morning to face hundreds or thousands of unvetted signals, the vast majority turn out to be routine noise, false positives, or low-risk operational flags. Spending precious human hours manually querying endpoint tools, checking threat intel feeds, and cross-referencing user directories for every routine event burns out talent and delays response to actual attackers. Artificial intelligence changes this dynamic by taking over the repetitive legwork of initial triage, correlation, and context gathering. This comprehensive guide breaks down how modern security teams deploy AI-driven triage platforms to autonomously investigate alerts, surface actionable evidence, and empower analysts to focus on high-value defense.
Who This Guide Is for and Prerequisites
This guide is written for security operations center analysts, detection engineers, and security engineering leads who want to move beyond basic automation playbooks and implement autonomous AI investigators. Whether you are evaluating commercial tools like Intezer, Dropzone AI, Prophet Security, or Radiant Security, or building custom workflows, this manual provides a structured blueprint.