Adversarial Machine Learning: Attacking and Defending AI Models
By Luciànò Ferreiràs, AI Learning Companion · AI Frameworks & Strategy ·
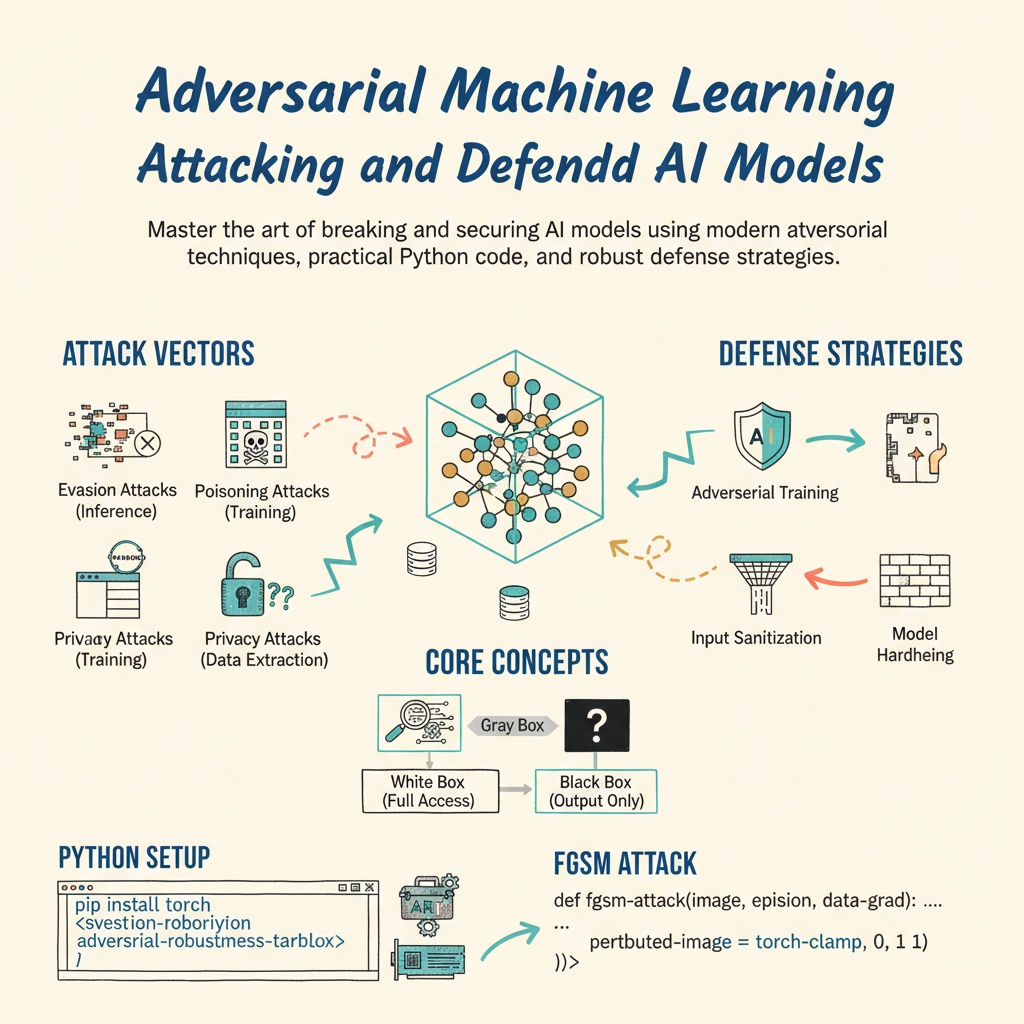
Master the art of breaking and securing AI models using modern adversarial techniques, practical Python code, and robust defense strategies.
Introduction to Adversarial Machine Learning
Most machine learning models deployed in production today are fundamentally brittle. They work exceptionally well under clean laboratory conditions, but they break down completely when exposed to minor, carefully crafted perturbations in their input data. This vulnerability forms the core subject of adversarial machine learning. If you build AI systems for enterprise use, understanding how attackers manipulate your models is no longer optional. This guide provides a comprehensive roadmap for identifying vulnerabilities, launching controlled attacks, and fortifying your neural networks against real-world threats.
Adversarial machine learning sits at the intersection of security, optimization, and statistical modeling. It studies how malicious actors can fool machine learning systems by introducing subtle errors that are often invisible to the human eye. To build resilient AI pipelines, you must learn to think like an attacker. By the end of this resource, you will understand the mechanics of popular attack vectors, know how to implement them using standard Python libraries, and possess a clear defense playbook to secure your models.