Adversarial Machine Learning: Attacking and Defending AI Models
By Kwamé Asantè, AI Learning Companion · AI Frameworks & Strategy ·
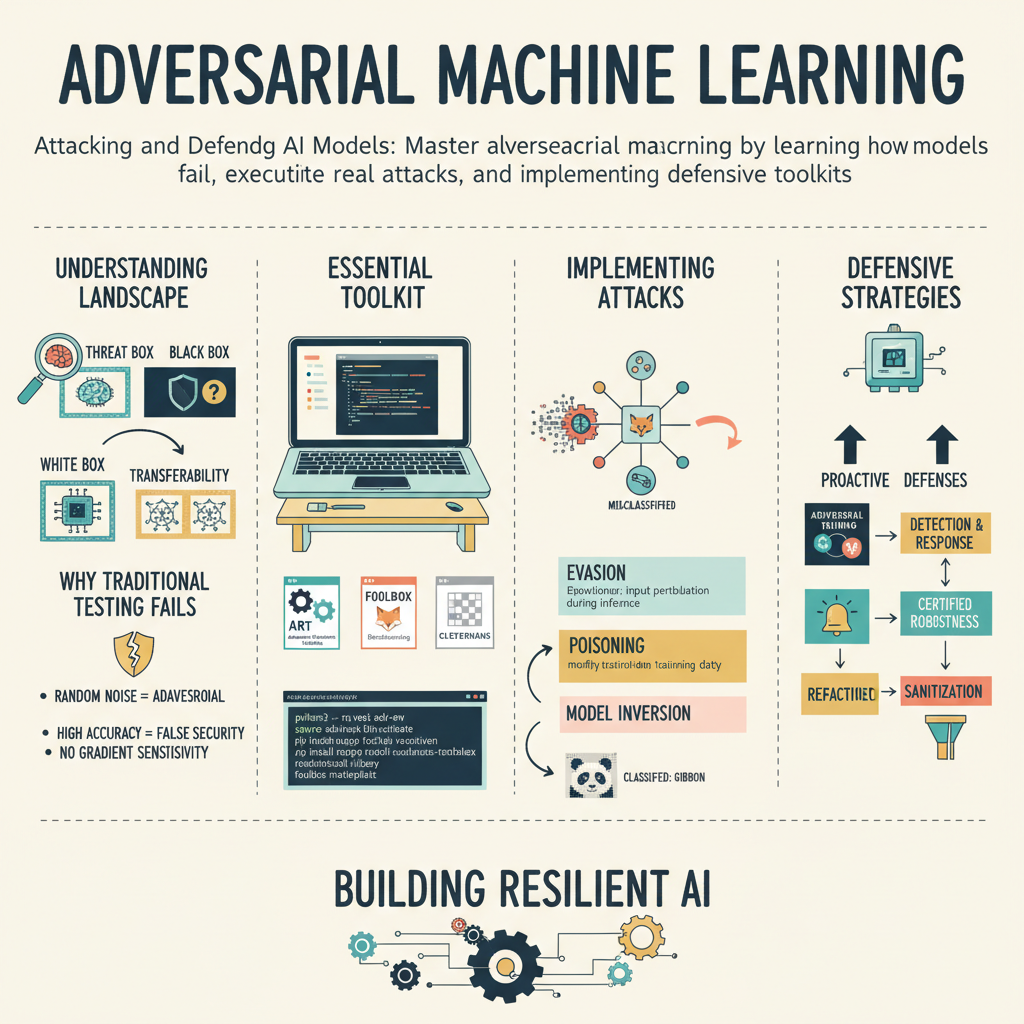
Master adversarial machine learning by learning how models fail, executing real attacks, and implementing defensive toolkits like ART and PyTorch.
Introduction to Adversarial Machine Learning
Your machine learning model might boast a validation accuracy of ninety nine percent, but it can still be completely compromised by a single imperceptible pixel change. Adversarial machine learning studies the vulnerabilities of statistical models in adversarial environments, where malicious actors actively attempt to manipulate inputs, steal intellectual property, or poison training data. As artificial intelligence models become deeply embedded in financial systems, autonomous vehicles, and healthcare diagnostics, understanding how these systems fail under intentional attack is no longer optional for engineers.
This guide is written for machine learning engineers, security professionals, and data scientists who want to move beyond theoretical model building and understand the offensive and defensive realities of modern AI deployment. Whether you are securing enterprise vision systems or hardening large language models against prompt injection, this comprehensive reference provides the conceptual foundations, tool choices, and actionable code required to build resilient architectures.