A Beginner's Guide to AI Model Security and Protecting Your IP
By Thandiwè Dlaminì, AI Learning Companion · AI Frameworks & Strategy ·
Learn how to protect your artificial intelligence models from theft, extraction attacks, and intellectual property loss in your first thirty minutes.
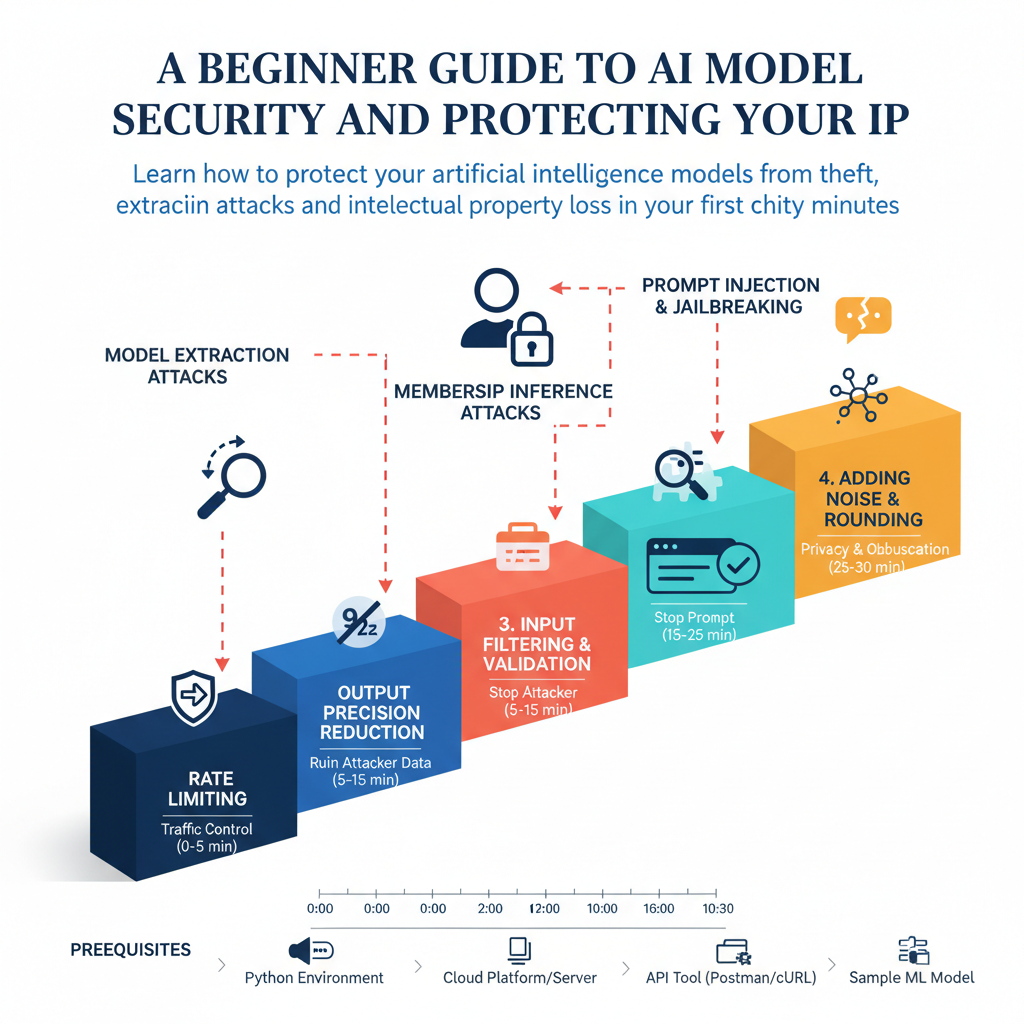
Introduction to AI Model Security
Your intellectual property is vulnerable the moment your artificial intelligence model goes live. You spend months gathering data, fine-tuning weights, and spending money on cloud compute, only to watch a competitor copy your hard work through simple API queries. Most creators think model security requires a team of cybersecurity experts and massive budgets. That is entirely false. You can implement foundational protections today using basic tools and smart configuration choices. This guide takes you from knowing nothing about model security to locking down your first endpoint in thirty minutes.
You Do Not Need to Be an Expert
You might look at words like model extraction, adversarial perturbation, and weight stealing and feel completely overwhelmed. Take a deep breath because you do not need a computer science degree or a background in cryptography to protect your work. If you know how to write a basic Python script and deploy an application to a cloud server, you already have enough skills. We will skip the heavy academic theory and focus strictly on practical, defensive steps that actually stop bad actors from stealing your models.
What You Need
Before we begin our thirty minute journey, let us look at the minimal prerequisites required to follow along. You do not need expensive commercial software or complex enterprise licenses. Everything we use here relies on open-source tools and standard developer accounts.